meet the team
Lucas Jansen
Security GRC Lead
“The thing I’d want clients to know about LeftBrain is that we genuinely care — not just about meeting the standard, but about actually improving your security.”
.
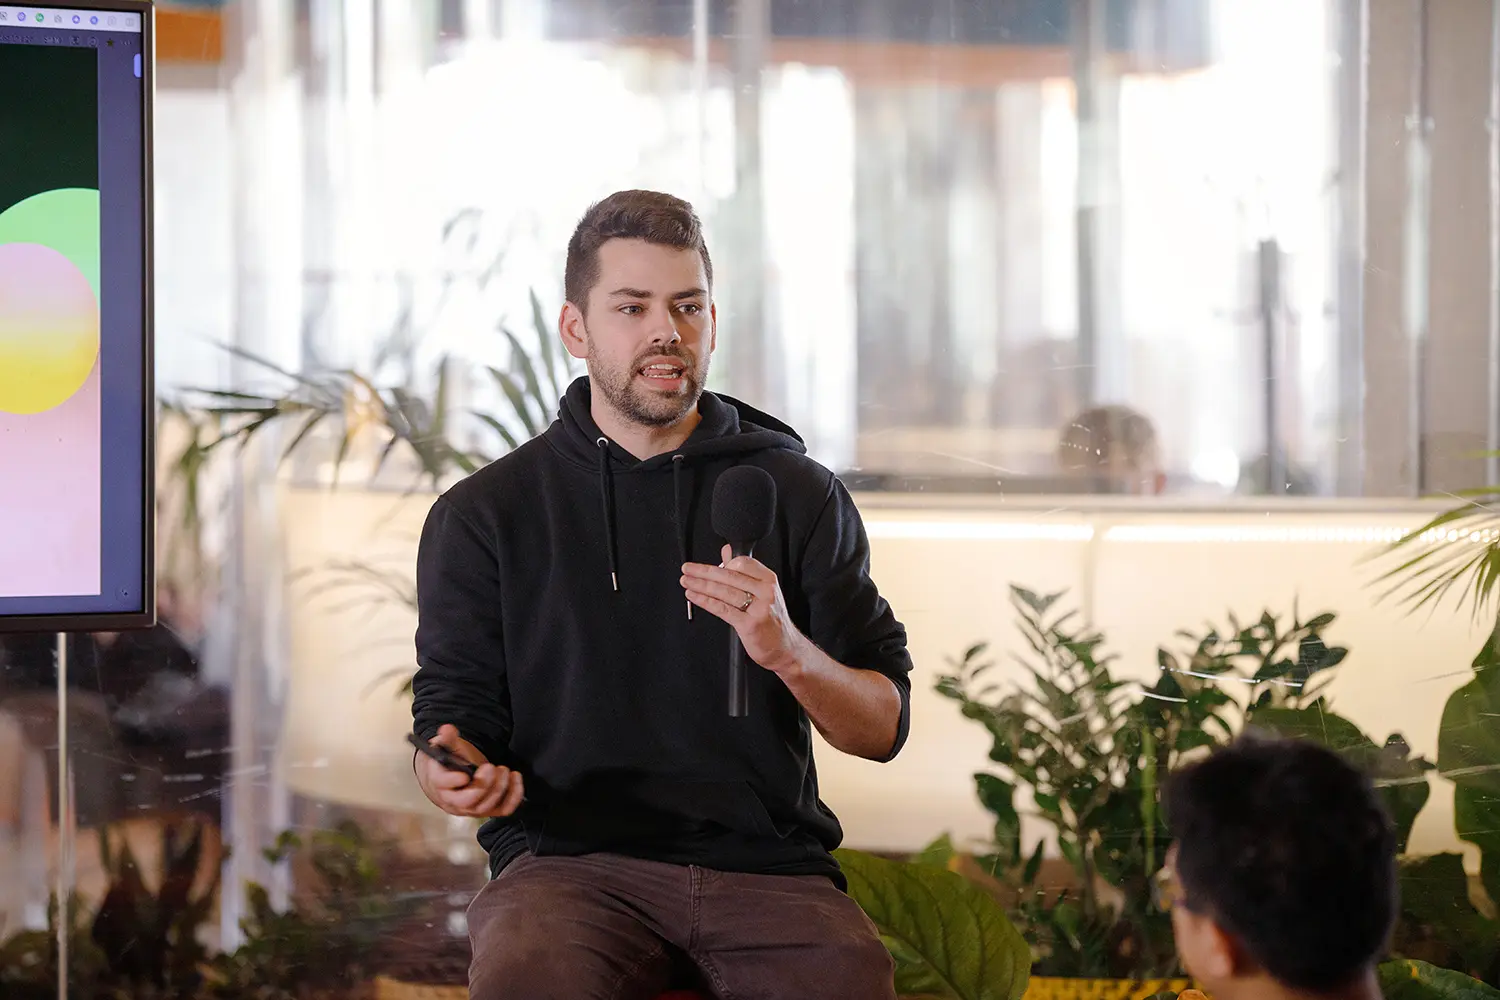
Composer of systems, not just music
Lucas is LeftBrain’s Information Security GRC Lead, handling governance, risk, and compliance day to day — building information security management systems aligned with standards like ISO 27001, SOC 2, and Cyber Essentials, supporting clients through auditor questionnaires, and making sure policies match what’s actually happening technically. He’s also the team’s resident Notion expert, having built much of LeftBrain’s own ISMS on the platform. Before cyber security, Lucas was a music teacher, and that background still shows: the same creativity that goes into organising a clear system once went into composing music, and the same skill of explaining something five different ways until it lands is exactly what’s needed to translate jargon into something clients can act on.
- ISO/IEC 27001:2022 Lead Implementer
- CompTIA Security+
- Jamf Certified Expert
- Practitioner Cyber Security Professional (PraCSP)
Get to know Lucas…
Latest from Lucas
The three ISO 27001 mistakes we see SMBs make most often
Struggling with ISO 27001 audits? Our GRC Lead shares the three mistakes SMBs make most often, and how year-round compliance keeps you audit-ready.
Read story
What we learned helping clients through the latest Cyber Essentials audits
Explore key lessons from recent Cyber Essentials audits with creative and remote-first teams. Learn how to reduce risk, improve visibility, and build strong security foundations without complexity.
Read story
How to prove trust fast with cyber security audit readiness
A founder’s guide to Cyber Essentials, ISO 27001 and government-assured cyber security
Read story
Meet Lucas’s team of security experts
Meet the team behind strategy and security advisory.